The Privacy Operations Platform
Privacy You Can Prove.
PrivTrust turns consent, data rights and privacy operations into enforceable controls and verifiable evidence, with the sensitive data itself protected in the same platform.
- Consent
- Data Requests
- ROPA
- DPIA
- Breach
- Data Protection
Privacy Operations
Good morning, Privacy Office
Active consents
0
+2.4%
Open data requests
0
92% on track
Signed records today
0
All verified
Processing activities
0
8 due review
Consent activity · 14 days
Privacy events
- Consent granted · Marketing · Webnow
- Consent withdrawn · SMS · App2s
- Evidence anchored · 1,024 records4s
- Erasure routed to 4 systems6s
Built for regulated organizations
- India DPDP Act
- Banking & Financial Services
- EU GDPR
- Healthcare
- Singapore PDPA
- Telecom
- 23 Official Languages
- Insurance
- Government & Public Sector
- SaaS Platforms
Privacy operations are fragmented.
Different teams. Different systems. No single control plane. So nobody can say, with evidence, whether a given use of personal data is allowed.
Know
what data you can use, and for which purpose.
Control
how it is used, in every system that touches it.
Prove
it when you're audited, without a scramble.
Marketing
Consent
Cookie banner
Legal
Data requests
Shared inbox
Compliance
ROPA
Spreadsheets
Risk
DPIA
Word documents
Security
Breach response
Ticketing
IT
Data protection
Another vendor
One privacy control plane.
Consent becomes a policy. The policy is enforced everywhere. Every decision becomes proof.
Step 1
Consent captured
- PurposeLoan servicing
- DataName, phone, PAN
- Duration24 months
Step 2 · PrivTrust
Policy enforced everywhere
Every system asks before it processes. Out-of-purpose use is denied at runtime.
Step 3
Verifiable proof
record cr_8f2a…91c
decision enforce
signature valid ✓
anchored yes ✓
Independently checkable by auditors and regulators.
From fragmented to provable, in five steps.
Start with a manual console workflow that is already compliant, then automate system by system at your own pace.
- 01
Connect your systems
CRM, ERP, apps, data platforms and identity systems, through APIs, webhooks, SDKs or your discovery tool.
- 02
Define privacy policies
Consent, purpose, retention, rights and processing activities, each with an accountable owner.
- 03
Enforce automatically
Every relevant event is evaluated against policy before data is used, by people, systems or AI agents.
- 04
Respond to data requests
DSR workflows route to the right systems and owners, automated or manual, per system, with deadlines tracked.
- 05
Prove compliance
Signed, tamper-evident evidence for auditors, regulators and security teams, ready on demand.
Everything your privacy team needs. In one place.
Two capabilities, one platform: Privacy Orchestration proves you have the right to use data. Data Protection secures the data itself.
Privacy you can prove, not just claim.
Audit logs ask auditors to trust you. PrivTrust evidence lets them check for themselves.
Signed, not just stored
Every consent grant and withdrawal produces a cryptographically signed record, not a database row.
Independently verifiable
A public verification tool lets auditors, regulators or your security team check any record themselves.
Tamper-evident by design
Entries cannot be altered or deleted once written, and are anchored to an independent timestamping service.
Consent receipt
cr_8f2a…91c{
"principal": "dp_41c9…e07",
"purpose": "loan-servicing",
"fields": ["name", "phone", "pan"],
"action": "granted",
"language": "hi-IN",
"expires": "2028-09-27",
"signature": "MEUCIQDx7…Qp4=",
"anchor": "tsa://…/2026-09-27T10:42Z"
}- Record hash matches
- Signature valid
- Timestamp anchor confirmed
Verified independently ✓
The privacy layer for AI agents.
Your agents access personal data only when the person has authorized that purpose, and every decision is auditable.
- Native MCP server: check consent for one user, in bulk, or discover the purposes your notice defines.
- Checked per data field, so an agent can be denied "email" and still allowed "name".
- Every agent decision lands in the same audit trail as a human request.
agent.request
read name for support-ticket
Not a banner. Not a binder. A control plane.
Consent tools stop at collection. GRC tools stop at documentation. PrivTrust enforces the policy and proves it.
Scope
CMPConsent banners
GRCCompliance documentation
Consent + privacy operations
Enforcement
CMPLimited
GRCMostly workflow
Runtime, per purpose and field
Evidence
CMPBasic logs
GRCDocument repositories
Signed, verifiable records
Regulations
CMPOften region-specific
GRCDocumentation-heavy
DPDP, GDPR and PDPA natively
Data protection
CMPSeparate vendor
GRCSeparate vendor
Built-in vault
AI agents
CMPNot covered
GRCNot covered
Consent checks over MCP
Operations
CMPManual
GRCHuman-heavy
Automated, system by system
Drops into the stack you already run.
API-first by design. Integrate one system at a time, automate when you're ready, and keep your existing data-discovery tooling.
- REST APIs
- Two-way webhooks
- Native MCP server
- React · Angular · JS SDKs
Enterprise-ready
- 99.99% SLA uptime
- Multi-region, regional data residency
- High availability, failover-ready
- 24/7 enterprise support
curl -X POST https://<your-tenant>/api/v1/consent-validation \
  -H "X-Client-Id: <client-id>" \
  -H "X-Client-Secret: <client-secret>" \
  -d '{
    "user_id": "user-42",
    "purposes": ["marketing"],
    "data_items": ["email"]
}'Built by people who have secured data at national scale.
Our leaders and advisors have architected security for Aadhaar, co-created India's eSign framework, led MOSIP identity infrastructure and led enterprise cybersecurity as an award-winning CISO. PrivTrust brings that experience to privacy operations.
- Digital Identity
- Cryptography
- Cybersecurity
- Privacy
- Risk & Compliance
- years architecting national-scale identity and digital infrastructure, our CTO
- 15+
- years architecting national-scale identity and digital infrastructure, our CTO
- identities on MOSIP, the platform our CTO helped architect
- ~200M
- identities on MOSIP, the platform our CTO helped architect
- years of global cybersecurity leadership as a CISO, now our CPO
- 24+
- years of global cybersecurity leadership as a CISO, now our CPO
- cybersecurity leadership awards, incl. Singapore Cybersecurity Awards 2024
- 6
- cybersecurity leadership awards, incl. Singapore Cybersecurity Awards 2024
Vishwanath Vaidyanathan
CTO · ex-Principal Architect, MOSIP
Anil Kumar Appayanna
CPO · award-winning CISO, 24+ years
Sasi Kumar Ganesan
Advisor · ex-Chief Security Architect, Aadhaar
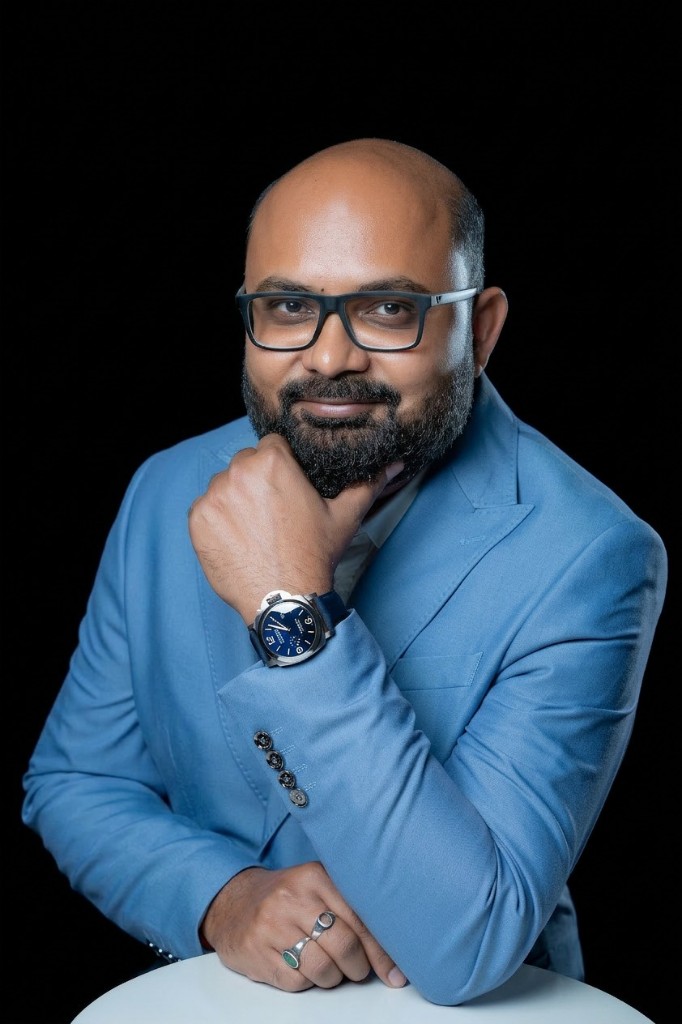
Sambit Garnaik
Advisor · cybersecurity entrepreneur
Ready to operationalize privacy?
See consent, data rights and evidence working together on your own use cases, with the sensitive data protected in the same platform.
- A walkthrough mapped to your systems
- DPDP, GDPR and PDPA coverage review
- Architecture Q&A with our engineers